
Table of Contents
SMS Authentication – 2-Step Verification
As a developer, you might find yourself wondering: are my tools, websites, and software secure enough? SMS two-factor authentication is a simple answer to the hacking and phishing attacks that have become commonplace in the web world.
Private data shared in the cloud is under constant risk.
3 reasons to authenticate users via SMS
E-commerce has exploded over the last 5 years, bringing with it the potential to fall victim to hackers looking to exploit your customers' private information. Without security measures like two-factor authentication, your software, websites, and applications are vulnerable to these security breaches.
Two-factor user authentication is essential during online data-sharing steps such as registration, new user account validation, or accessing user accounts and servers that contain sensitive information (phone numbers, bank details, etc.).
In a world where data security can make or break a company's reputation, it is vital to seek a reliable two-factor authentication solution so that your users' data is never compromised.
What does it take to enable two-factor authentication?
Enabling two-factor authentication on your application, software, or website is a relatively simple process.
You have likely already implemented the first step: a username and password. To set up the second step, you will need to decide where and how users will receive this one-time password to confirm their identity.
The easiest and most popular choice for this is SMS, simply because most users use their mobile phones for everything they do. Web developers have learned to neutralize this threat with efficient SMS services.
Requiring your users to register in two steps helps protect their accounts from hacking and protects your business.
You can build your authentication system in-house if you are feeling adventurous, or create it using an open-source solution or a full-service provider. Google Authenticator is an effective option and can be integrated with your SMS API. The application will generate a unique code for you on demand, which the user must provide during authentication in addition to their login and password.
What should I look for in an SMS provider?
The SMS service you choose for your two-factor authentication can be just as important as the implementation of the service itself. Make sure the provider you choose offers coverage where your users reside and can handle the volume of traffic you will generate. You should also ensure the service will work with your code.
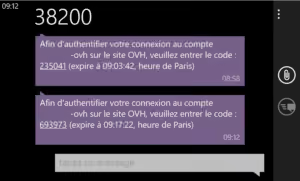
Once integrated, you will be able to authenticate your users via SMS. This means that when they want to use your application or create an account on your site, instead of just entering a standard password, they will also need a password sent to them via your secure SMS system.
Two-factor authentication proves to your customers that you provide effective security solutions for this modern problem.
In fact, user authentication via SMS has become a standard security practice. Google, Facebook, Twitter, and Apple have all implemented two-factor authentication to better identify their users.
SMS authentication is also an integral part of setting up a WhatsApp account on your mobile phone.
User authentication via SMS is much less expensive than implementing a hardware-based solution. Your app users already have a mobile phone: why not use it?
Is two-factor authentication a complete solution?
While this type of authentication process is effective for security, it is not foolproof. A user's phone could be lost or stolen, for example.
Companies selling products or services online must, however, have this feature if they want to remain competitive in the global market. Therefore, even though two-factor authentication has its flaws, it remains the most reliable solution for securing your customers' information.